

JFrog Security Real Time Posts
Last Updated On 9 Nov, 2026
JFrog Security researchers have identified new, previously unreported compromised package versions related to the CanisterWorm npm supply chain attack.
The JFrog security research team recently encountered 2 malicious packages on the NPM ecosystem, delivering via Dropbox links a windows executable. While checking these files in VirusTotal shows almost no Anti Virus (AV) results that flag it, the behavior analysis showed suspicious activity, leading us to dive in.
The JFrog Security research team has identified a malicious npm package named @openclaw-ai/openclawai. This package masquerades as a legitimate CLI tool called "OpenClaw Installer" while deploying a multi-stage infection chain that steals system credentials, browser data, crypto wallets, SSH keys, Apple Keychain databases, iMessage history, and more
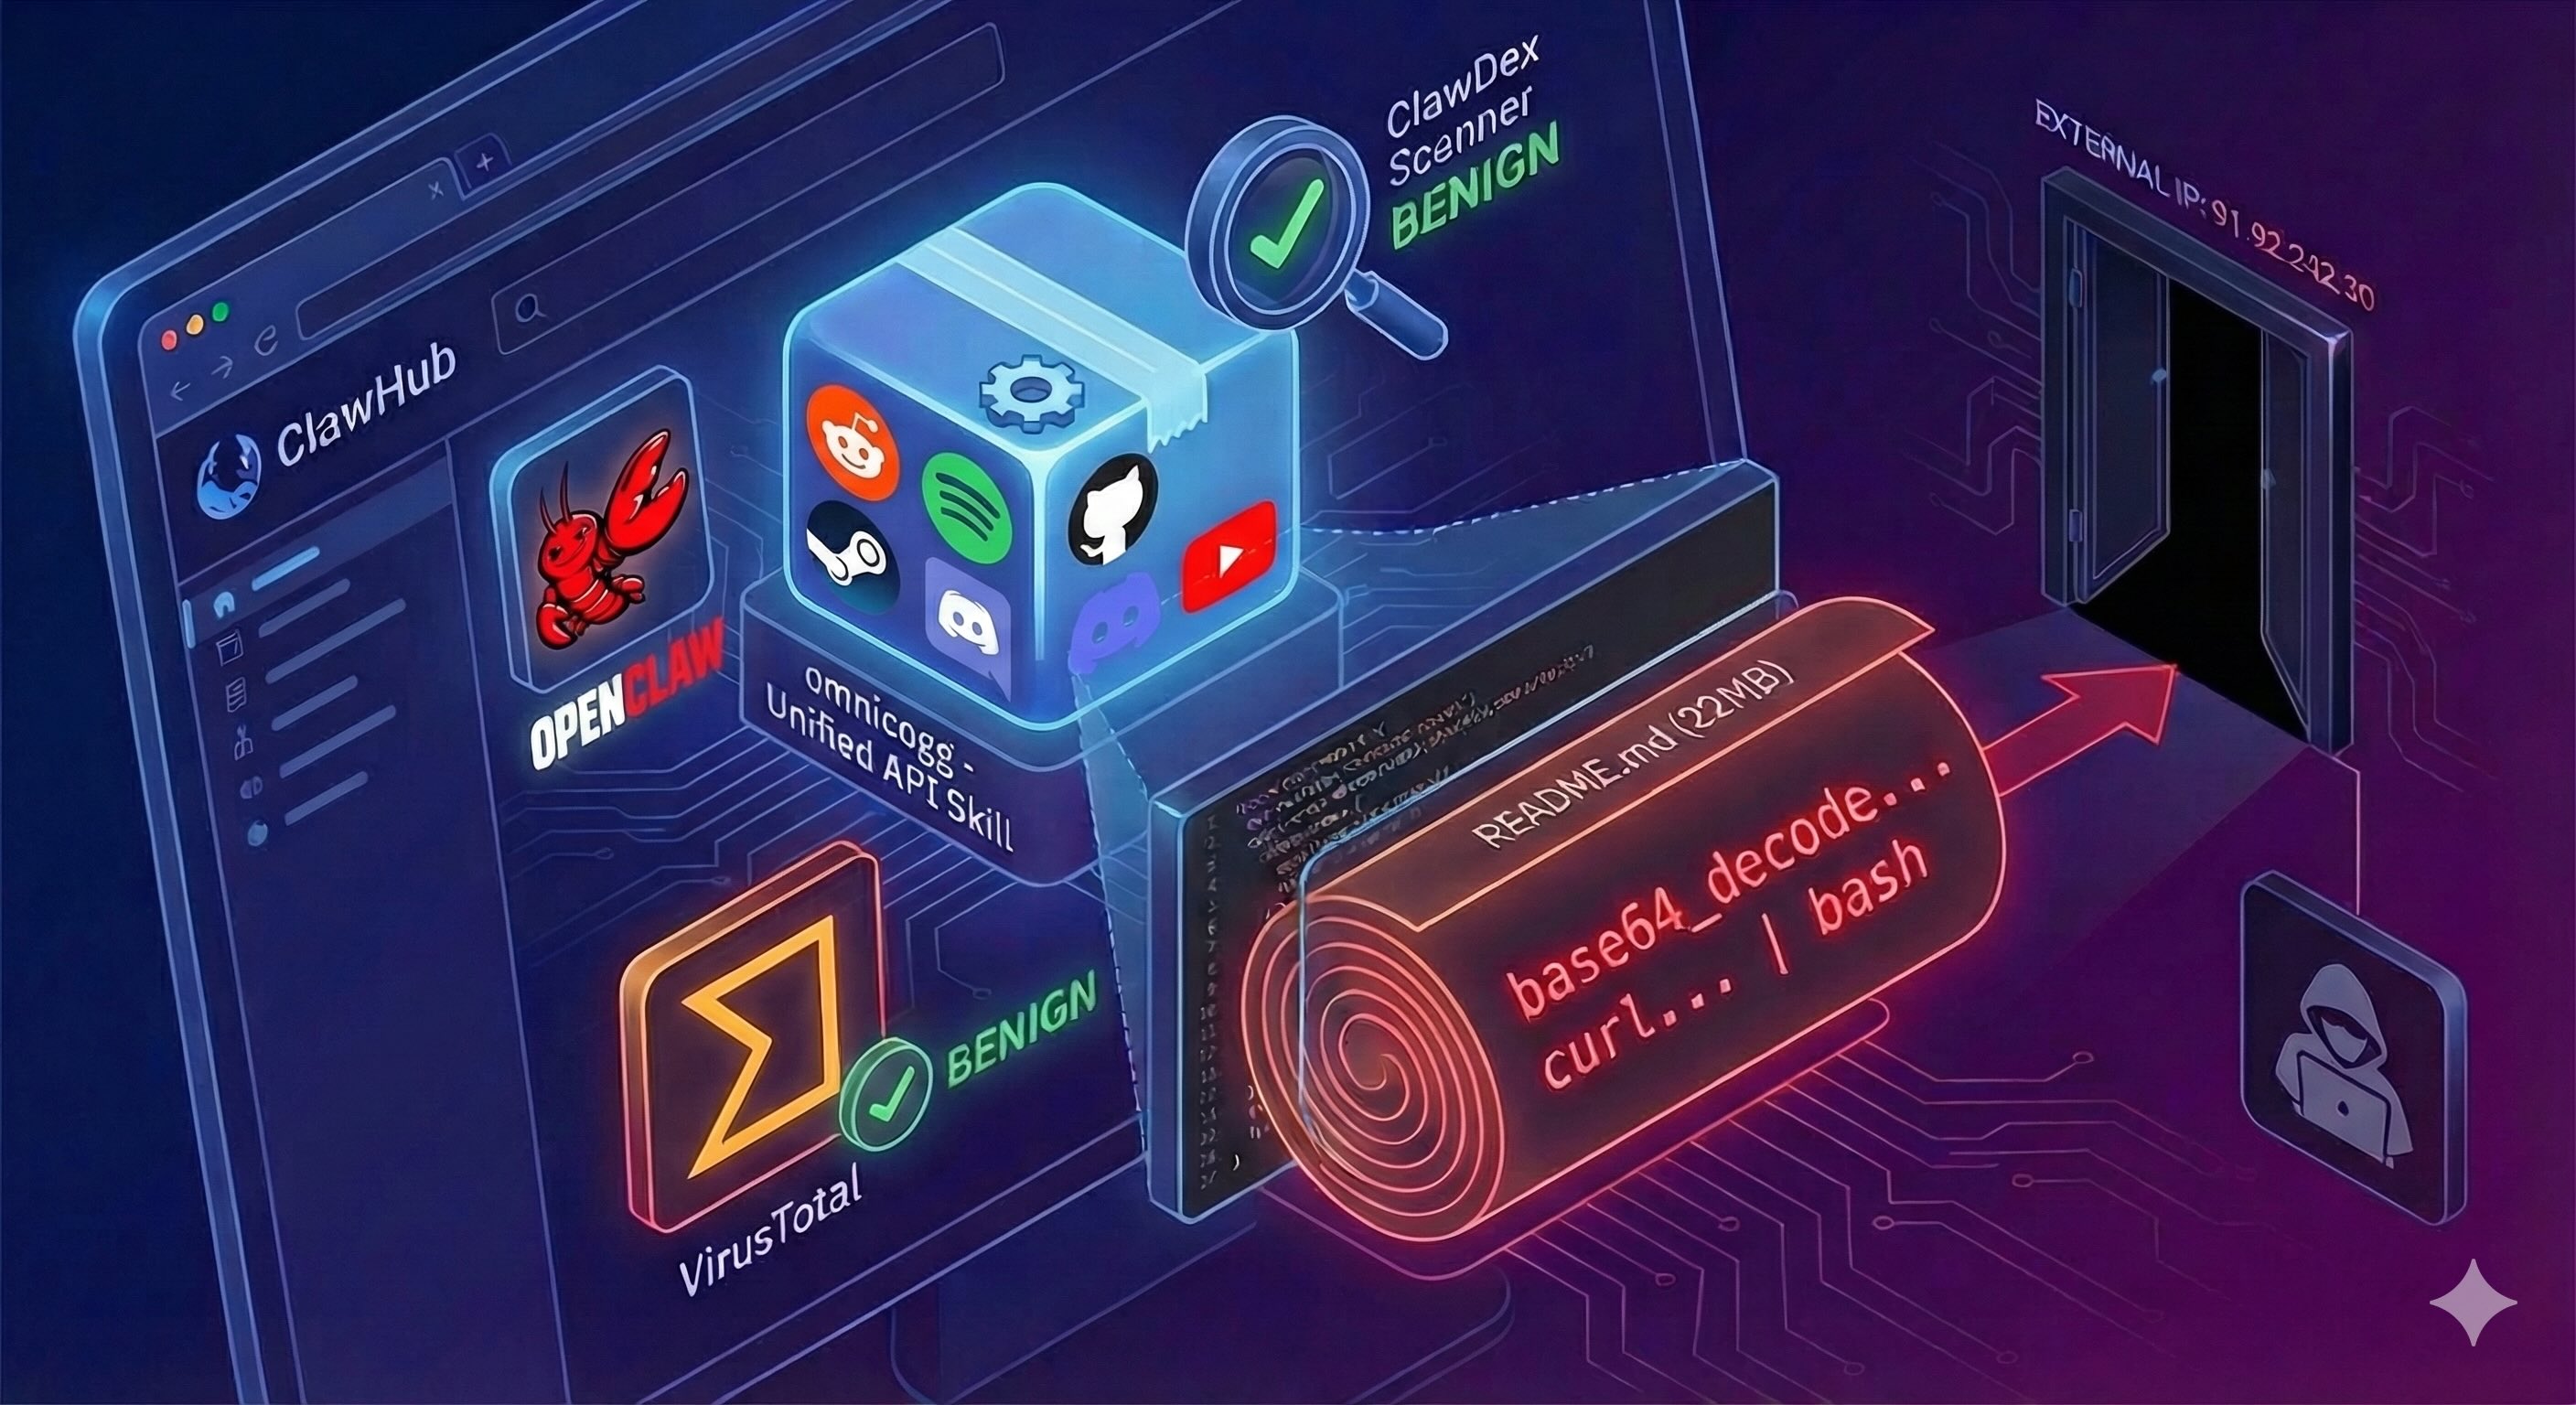
The JFrog Security Team has identified a malicious OpenClaw skill named omnicogg hosted on ClawHub that uses a 22MB padded README to hide a base64-encoded RCE dropper, bypassing VirusTotal, ClawDex, and ClawHub's own scanner to harvest developer credentials.
Our research team found multiple vulnerabilities in OSS CI workflows, in this blog we cover the “Test-Based Execution” exploitation pattern.
Our research team found multiple vulnerabilities in OSS CI workflows, in this blog we cover the “Build-Scripts and Installer-Based Execution” exploitation pattern.
Our research team found multiple vulnerabilities in OSS CI workflows, in this blog we cover the “Branch and Config Injection” exploitation pattern.

The JFrog Security Team has identified a malicious npm package named eslint-verify-plugin that deploys a sophisticated multi-stage infection chain, ultimately delivering a full-featured Mythic/Apfell macOS RAT capable of credential theft, screen capture, and backdoor account creation.
The JFrog security research team recently uncovered a sophisticated malicious package called "duer-js" published on NPM by the user "luizaearlyx". After complex analysis, the package was identified as an advanced windows targeted information stealer, self-named as “bada stealer”. The package remains active as of this publication.
The JFrog Security Research team is tracking a newly disclosed OpenSSL vulnerability, CVE-2025-15467, a stack overflow issue that may lead to remote code execution (RCE).